
API keys connect your own scripts and tools to your Argorant account. This page covers looking after them: how many to have, how to replace one, and how to switch one off the moment you no longer trust it.
Where your keys are
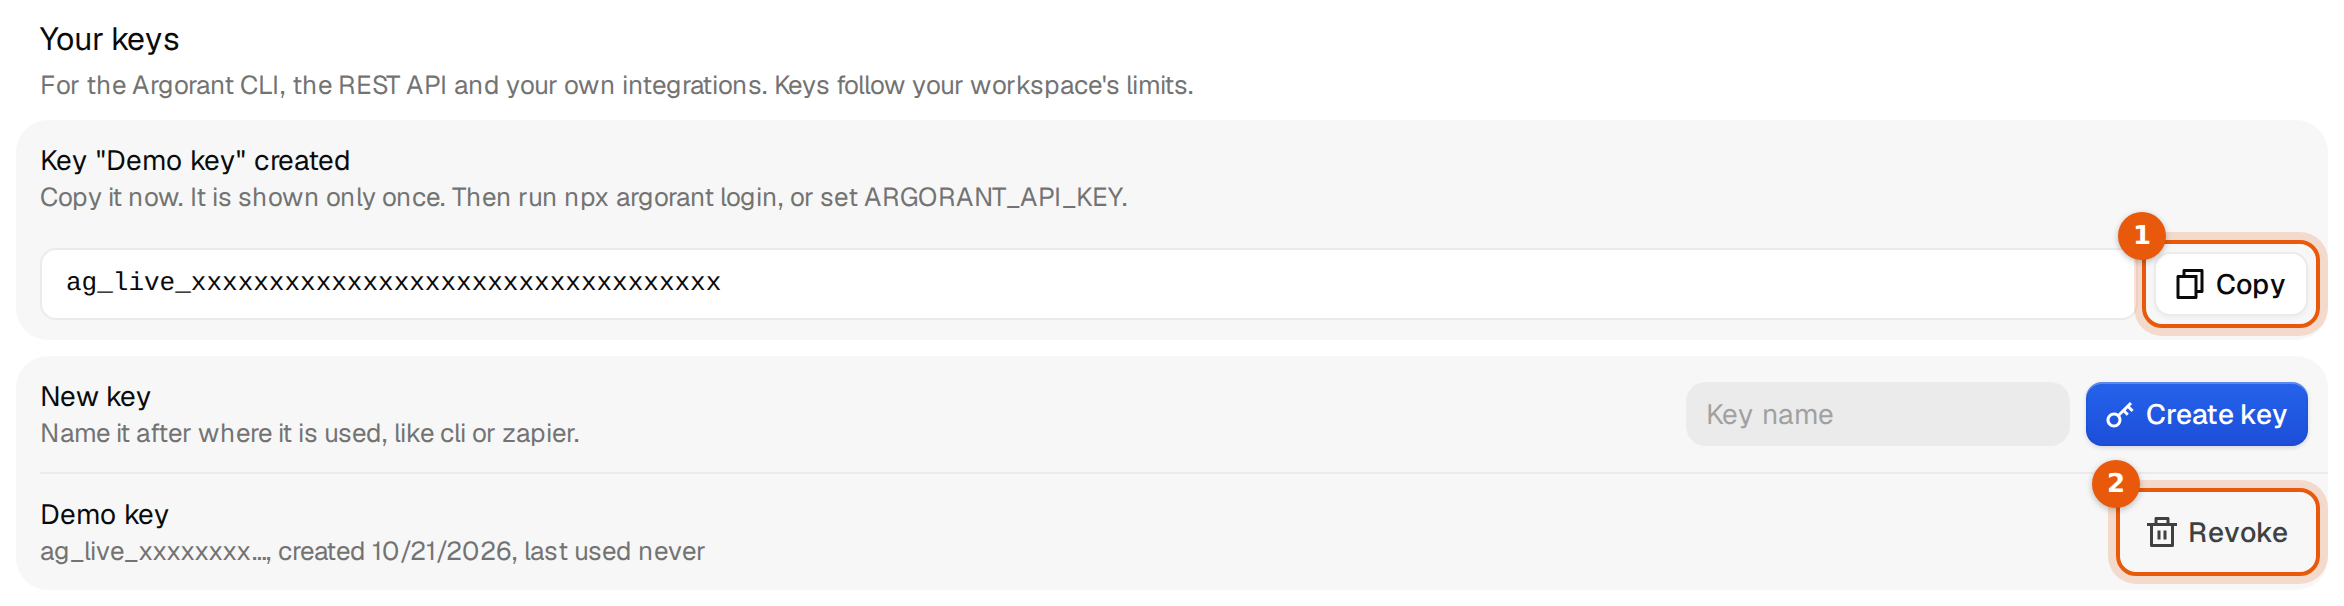
Open Settings, then API keys. Under Your keys each key has one row with its name, the first characters of the key, the day it was created and the day it was last used. The full key is never shown again after it was created.
One key per tool
Create a separate key for every place that uses one: cli-laptop, zapier, n8n-prod, claude-code. It costs nothing and gives you three things.
- You can switch off one tool without breaking the others.
- The last used date tells you whether a tool still runs.
- Each key has its own requests per minute, so a busy automation does not slow down your terminal.
Names may use letters, digits, spaces, dots, dashes and underscores, up to 64 characters. Without a name the key is called default.
Replace a key (rotation)
Creating a key with a name that already exists replaces that key. The old key stops working at once and the new one appears in the box. That is the quickest way to rotate.
- Have the place where the key is stored open, for example the CI secret, the Zapier step or your
.envfile. - In Settings, type the exact name of the key and click Create key.
- Click Copy and paste the new key into that place.
- Run one call to check it, for example
npx argorant whoami.
Between step 2 and step 3 the tool runs without a working key. If it must not stop even for a minute, create the new key under a new name first, switch the tool over, then revoke the old one.
Revoke a key
- Click Revoke in the key's row.
- Confirm with Revoke key.
Anything using it stops working immediately. This can't be undone.
The next request with that key answers 401, and the CLI exits with code 2. Lists, exports and credits are untouched; they belong to your account, not to the key.
Revoke every key at once
Under Settings, then Workspace, the Danger zone has Revoke all API keys. Every CLI, script and integration that uses a key stops at once. Signed-in sessions and AI connections stay. The opposite button, Sign out everywhere, ends sessions and AI connections but leaves keys working, so after a leak you may want both.
What a key may do
A key from Settings can count and search, manage lists and campaigns, create exports, reveal contacts and check your own addresses. It follows your workspace's plan, credits and limits, and your own role in the workspace. There is no switch per key to leave out spending. If an agent should only count and search, tell it so in its instructions and keep your balance small, or give it the connector, where you approve each permission. Run npx argorant whoami to see the permissions of a key.
Common mistakes
- The key was lost. Nobody can show it again. Create a new one under the same name, which also switches the lost one off.
- The key was pasted into a chat, a ticket or a repository. Treat it as leaked. Revoke it and create a new one. See If an API key leaks.
- Revoked, but the CLI still works. Another key is set in
ARGORANT_API_KEYor saved byargorant login. Runargorant logoutand unset the variable. - A teammate's tool broke. Keys belong to the person who created them. Ask them to create their own key instead of sharing yours.
What happens next
A new key works the moment it is created. To put it to use, read API keys and the REST API or the Argorant CLI.